Category: Best Practices for Merchants
January 13th, 2016 by Elma Jane
If you’re a travel merchant or any merchants using Internet Explorer we want to share this information with you.
As Microsoft ends support for anything older than Internet Explorer 9 (IE9), security experts urged IT managers to migrate to newer versions of Internet Explorer to avoid risk exposing themselves to a new wave of attacks.
Back in August 2014, IEBlog shared important information on migration resources, upgrade guidance, and details on support timelines.
After January 12, 2016, only the most recent version of Internet Explorer available for a supported operating system will receive technical support and security updates.
Vista SP2 and Server 2008 SP2 users will only be supported on IE9; Windows 7 SP1, Windows Server 2008 R2 SP1, Windows Server 2012 R2 and Windows 8.1 users will need to upgrade to IE11; and Windows Server 2012 customers will need to migrate to IE10.
This will apparently ensure they get the benefit of Microsoft security updates and technical support.
Internet Explorer is one of the most commonly targeted platforms in the world for cyber-criminals, businesses would do well to get their house in order. Staying on unsupported versions will have a serious impact on your business.
To know more about Support Lifecycle Information click here
Posted in Best Practices for Merchants Tagged with: merchants, travel, Travel Merchant
January 12th, 2016 by Elma Jane
Can we securely store card data for recurring billing?
PCI DSS discourages businesses from storing credit card data, Merchants feel the practice is necessary in order to facilitate recurring payments.
The Payment Card Industry Data Security Standard (PCI DSS) is a proprietary information security standard for organizations that handle branded credit cards from the major card schemes including Visa, MasterCard, American Express, Discover, and JCB.
In order for the electronic storage of cardholder data to be PCI Compliant, appropriate encryption must be applied to the primary account number (PAN). In this situation, the numbers in the electronic file should be encrypted.
All PCI controls would apply to the environment in which the cardholder data is transmitted and stored. Tokenization can be implemented for recurring and/or delayed transactions. Travel Merchants and or Storage Facility could use this feature to help reduce the need for electronically stored cardholder data while still maintaining current business processes.
The best thing you can do for your business is to not store any cardholder data or personally identifiable information.
Tomorrow let’s tackle Encryption and Tokenization a strong combination to protect card data while reducing the cost of compliance!
Posted in Best Practices for Merchants, Credit card Processing, Credit Card Security, Payment Card Industry PCI Security, Travel Agency Agents, Visa MasterCard American Express Tagged with: cardholder data, credit card, data, merchants, payments, Security, tokenization, transactions, travel
January 11th, 2016 by Elma Jane
Chase Commerce Solutions, the global payment processing and merchant acquiring business of JPMorgan Chase & Co., sold its entire portfolio of Independent Sales Organization (ISO) accounts and associated contracts.
Financial terms of the deal were not disclosed.
Chase has been decreasing the number of merchant relationships it supports through traditional ISOs and increasing the number of direct acquiring relationships it has with merchants since it formed Chase Merchant Services, a partnership with Visa that began 2013.
During that time it has focused more on e-commerce, reports said, though the biggest news for Chase Commerce Solutions recently was its agreement with Starbucks in November to take over processing of all its non-mobile payments.
Posted in Best Practices for Merchants Tagged with: Commerce Solutions, e-commerce, Independent Sales Organization, ISO, merchant, merchant services, Mobile Payments, payment processing, visa
January 7th, 2016 by Elma Jane
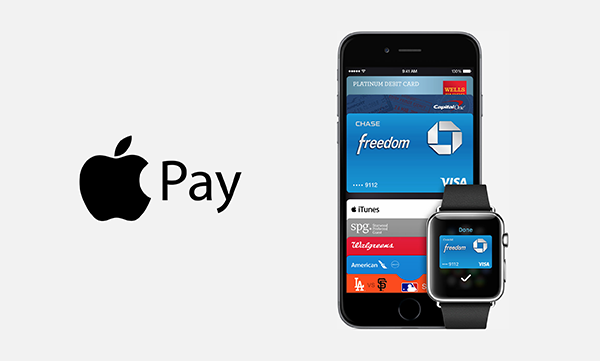
National Transaction is now offering Apple Pay to Canadian Merchants.
Apple Pay works with NTC’s EMV-contactless point of sale terminals in Canada.
Security and privacy is at the core of Apple Pay, and when a consumer adds a credit card to Apple’s mobile wallet, the actual card numbers are not stored on the device, or on Apple servers.
Apple Pay will create a unique Device Account Number that is assigned, encrypted and securely stored in the secure element on the device, the same way it operates in the U.S. Each transaction is authorized with a one-time unique dynamic security code.
To pay, consumers simply hold their mobile device near the contactless reader, exactly as they would a contactless card today. The payment information is then passed to the POS system once the consumer confirms the transaction using Touch ID on their device.
Bringing Apple Pay to NTC terminals addresses an increasing consumer demand for contactless payments, while also allowing Canadian businesses to offer customers the convenience of paying through an iPhone, iPad or Apple Watch.
American Express is Apple’s issuing partner in Canada.
Posted in Best Practices for Merchants Tagged with: Contactless card, contactless point of sale, contactless reader, credit card, EMV, merchants, mobile device, mobile wallet, payment, POS system, security code, terminals
January 6th, 2016 by Elma Jane
A company is teaming up with MasterCard to help other companies integrate mobile payments into their fitness devices, smart watches, jewelry, or clothing. Anything and everything that can fit an NFC chip inside it.
The program is a small iteration on something MasterCard announced last October, in which MasterCard was setting up essentially the same thing: Tokenized payment systems device makers could embed in virtually anything.
To start, the two companies have partnerships set up with Atlas, Moov and Omate, all of whom make wearable or fitness devices. The idea is that if you’re out for a run, you can just use the fitness band you’ve already got on you to buy something. That makes sense, but it also may mean you’ve got yet another payment system to set up and think about, one that presumably isn’t fully integrated either into your Apple Pay or Android Pay setup.
http://www.theverge.com/2016/1/6/10704812/coin-mastercard-partnership-ces-2016-atlas-wearables-moov-ornate
Posted in Best Practices for Merchants Tagged with: Mobile Payments, nfc, payment system
December 28th, 2015 by Elma Jane
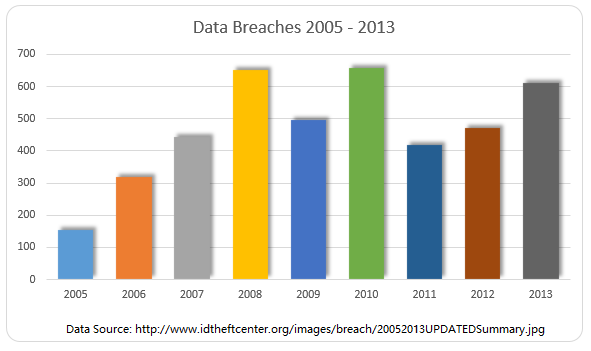
Major data breaches were acknowledged by another hotel chain and another brand popular with kids.
Hyatt discovered the intrusion on Nov. 30, which targeted Hyatt-managed properties (not those owned by franchisees), but did not disclose exactly how many properties were affected or how many records may have been exposed. The malware used in the attack targeted payment-card information including cardholder names, PANs, expiration date and CVV/CVC information.
Separately, a security researcher discovered a leaked database from Sanrio, the Japanese company that designs, licenses and produces the popular hello Kitty character. The database reportedly contains account data for 3.3 million users of Sanriotown.com and other Sanrio-owned Websites including hellokitty.com. The company has not yet acknowledged the extent of the breach publicly but said it is investigating.
If so, it is the second network intrusion made public putting the personal information of young people at risk after the Vtech Toy Company Data Breached. Almost 5 million parents and more than 200,000 kids was exposed. The hacked data includes names, email addresses, passwords, and home addresses of 4,833,678 parents who have bought products sold by VTech.
Posted in Best Practices for Merchants Tagged with: card, card information, data, data breaches, payment
December 21st, 2015 by Elma Jane
Chargebacks is a major problem for merchants, rules and regulations surrounding chargebacks can be confusing; becoming educated about these policies, which also includes the release of a new and upcoming regulations will help merchants to empower themselves.
Visa will make major changes to its chargeback rules document in January of 2016.
Traditionally, Visa has had two different excessive-chargeback programs for merchants:
1. For Domestic U.S. transactions – known as the U.S. Merchant Chargeback Monitoring Program.
2. For international transactions – called the Global Merchant Chargeback Monitoring Program.
Each program had a different threshold and monitored transactions in different geographic regions (each with unique risk profiles), it has been possible for a merchant to qualify for one program but not the other.
http://cardnotpresent.com/articles/displaylogin.aspx?id=12785
Posted in Best Practices for Merchants, Visa MasterCard American Express Tagged with: chargebacks, merchants, visa
December 21st, 2015 by Elma Jane
You will think United States or China are the two world’s biggest market when it comes to digital payments and other cashless spending systems. But according to a study, the answer is a less likely source: Sweden is actually on its way to becoming a fully cashless society.
Several factors have come together to give the Swedes an unexpected edge, a combination of IT awareness, and a growing number of useful mobile payments solutions.
The entire country currently only has about 80 billion Swedish crowns in circulation, and as users more often turn to mobile payment systems, the need for cash only declines. About 20 percent of all purchases made in cash in Swedish retail, and that number is falling off almost daily.
Some transactions can only be carried out by digital payments, since the mobile apps are convenient, free to use, and generally regarded as secure, there’s not much impediment for users to turn to such systems.
A truly cashless society is probably a bridge too far; there will always be those who’d rather handle cash. Only time will tell if the market shapes up looking like this, but even with lower actual results than projected, that’s still a lot of people turning to mobile payment and other cashless payment systems. There will still be a huge majority trending toward cashless society.
http://paymentweek.com/2015-12-18-world-leader-in-cashless-trading-an-unexpected-source-9182/
Posted in Best Practices for Merchants Tagged with: digital payments, mobile payment systems, Mobile Payments, mobile payments solutions, payment systems, payments solutions
December 18th, 2015 by Elma Jane
A leading provider of mobile point of sale and mobile payment technology, published today the EMV Migration Tracker.
Many merchants have deployed EMV capable terminals while cardholders have received cards with EMV chips, but not much data has been published about the real world use of EMV chip card technology in the U.S. Most published statistics rely on surveys or forecasts rather than real transactional data.
The EMV Migration Tracker shows new data and insights since the October 1 liability shift, including:
- Over 50% of all cards in use now have EMV chips on them. From October to November, the percent grew 5% as banks and card issuers accelerated their rollout of new chip cards.
- Over 83% of American Express cards have EMV chips, while Discover lags at 40%
- Over 63% of the cards used in Hawaii have EMV chips, but Mississippi sees just 11% penetration of chip cards.
While EMV chip card technology has been implemented in Europe years ago, the rollout of EMV in the U.S is just beginning. The rollout came earlier this year with the October 1 liability shift in card present transaction, meaning that merchants who have not upgraded their POS system can become liable for counterfeit card fraud losses that occur at their stores. This is an early step in an ongoing process that the Payments Security Task Force predicts will lead to 98 percent of U.S. credit and debit cards containing EMV chips by the end of 2017.
http://www.finextra.com/news/announcement.aspx?pressreleaseid=62506
Posted in Best Practices for Merchants Tagged with: American Express, banks, card issuers, card present, card technology, cardholders, chip cards, credit, data, debit, Discover, EMV, EMV chips, merchants, mobile payment, mobile point of sale, payment technology, point of sale, POS, provider
December 17th, 2015 by Elma Jane
We are pleased to announce that the new Converge Mobile App is now available for download in the App Store (Apple iOS devices) and Google Play (Android devices)!
Ingenico iCMP – Item code CICMP for Converge and Converge Mobile
With the launch of the new app, you can now order the Ingenico iCMP PIN Pad for Converge Mobile too!
Please use item code CICMP for those devices that will be used with Converge and Converge Mobile applications.
The Talech iCMP is configured differently and will not work properly without substantial reconfiguration work by our support teams. This creates a negative customer experience and is avoidable when you use the right code – CICMP!
Posted in Best Practices for Merchants Tagged with: Converge, Ingenico iCMP, mobile, Talech iCMP